Summary: Your IT budget should include the technology you already use, the support required to maintain it, and the upgrades you expect to make during the year. It should also cover cybersecurity, backups, employee changes, planned projects, and a reserve for urgent repairs or replacements. If your IT budget only covers computers, Microsoft 365, and […]
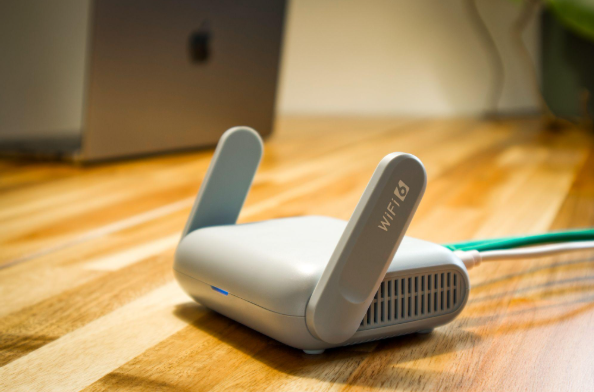
Summary: Guest Wi-Fi should provide internet access while blocking connections to your internal business network. A different Wi-Fi name and password do not confirm that the networks are separated. The router, access points, and firewall must also be configured to prevent guest devices from reaching internal systems. Offering Wi-Fi to customers, contractors, and visitors is […]
Summary: Allow personal devices only for approved work, through approved apps, and when the device meets your security requirements. Use company-owned devices for administration, sensitive work, or jobs that require large amounts of data to be stored locally. Employees often use personal devices for work before the business has made a decision about it. They […]
Summary: Employees should use standard accounts for email, web browsing, and everyday work. Administrator access should be limited to approved IT tasks and protected with a separate account. Administrator access often starts with one request. An employee needs to install a printer, update a specialist program, or change a setting on their computer. Giving them […]
Summary: Most IT problems don’t appear out of nowhere. Backups quietly stop running, updates sit unfinished for weeks, and old staff accounts stay switched on for months. A short check once a month catches these while they’re still cheap to fix. This post covers the six things to look at. Most owners only look at […]
By the time an employee hands in their notice, the decisions that will make their departure clean or messy have already been made. They were made in the first weeks of the person’s tenure, when nobody was paying close attention because the new hire had just arrived and there were a hundred other things to […]
Cyber insurance applications include a question that catches a lot of small business owners off guard: “Do you maintain immutable, air-gapped, or offline backups of your critical business data?” Carriers added that question to renewal forms because ransomware operators worked out that the fastest way to force a payout is to wipe the backups first […]
Someone leaves the company on a Friday. By Monday, their email account is disabled, and their laptop is back in the pile. What nobody checks is their login to the project management tool they signed up for in Q3, the cloud storage folder they shared with a contractor, or the CRM access they still have […]
The most time-consuming ticket in your queue is rarely a hardware failure. It’s the PC infection that started when a user installed something they shouldn’t have been able to. Or it’s the broken configuration left behind after someone changed a setting IT can’t trace. Local administrator rights (the ability to install software, modify system settings, […]
The most dangerous thing in a server room is often the phrase, “Don’t touch that.” It’s usually said with a half-joke and a grimace. It refers to the old box that “still works”, runs something important, and has survived so many fixes and workarounds that nobody feels confident changing it anymore. That’s legacy debt. Not […]
- 1
- 2